What You Will Learn
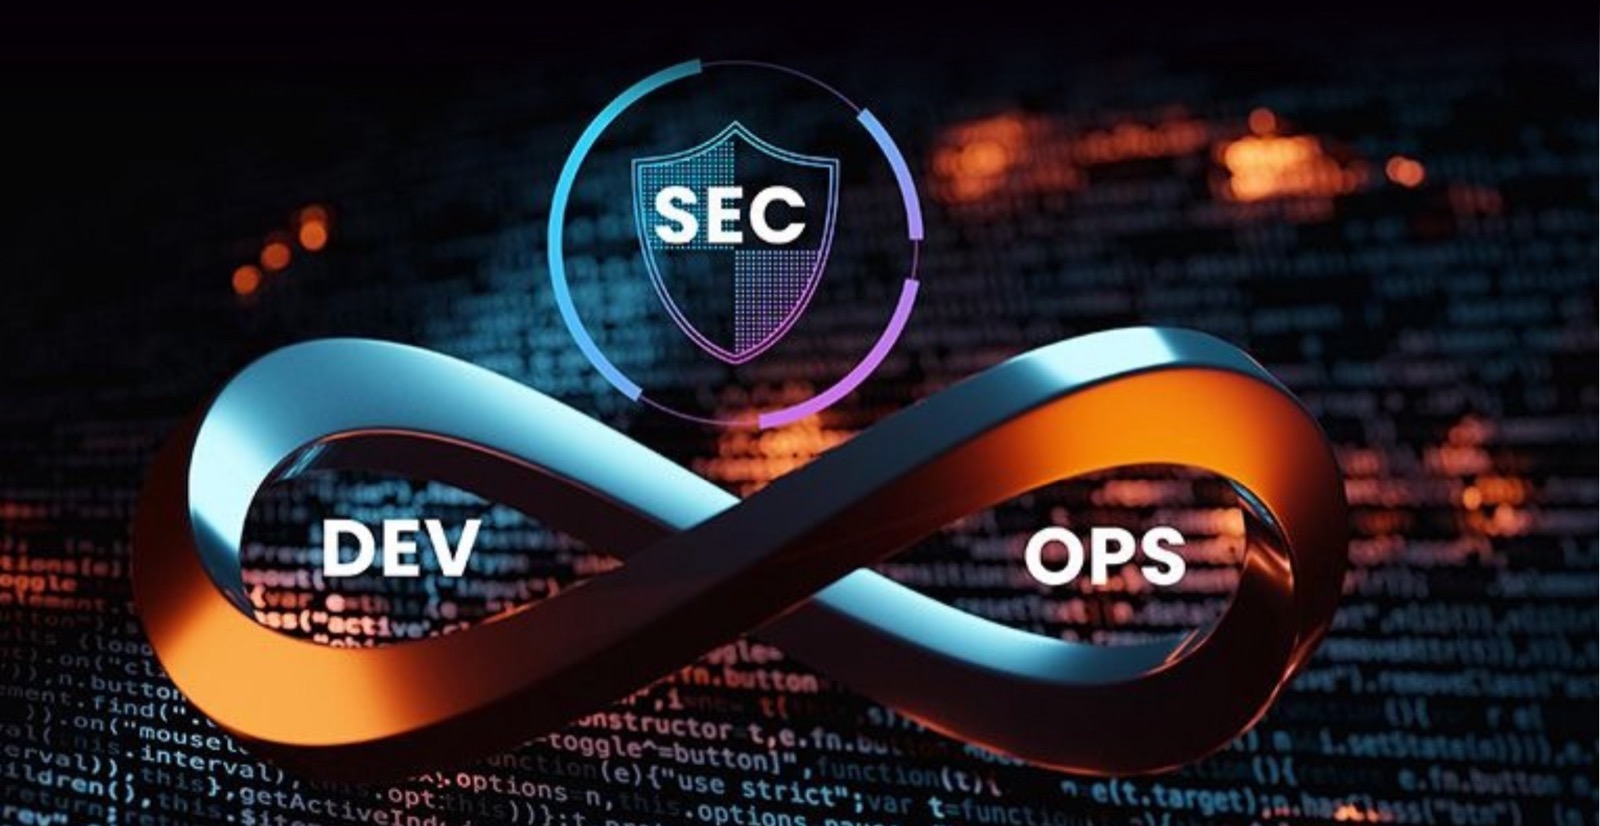
- DevSecOps Fundamentals: Understand the principles of integrating security into development and operations workflows and the benefits of shifting security practices earlier in the software lifecycle.
- Secure Software Development: Learn how secure coding practices, code reviews, threat modeling, and security requirements help reduce application vulnerabilities.
- CI/CD Pipeline Security: Understand how to secure continuous integration and continuous delivery pipelines, control access, protect build environments, and maintain software delivery integrity.
- Static and Dynamic Application Security Testing: Explore how SAST, DAST, and related testing methods help identify vulnerabilities in source code and running applications.
- Software Composition Analysis: Learn how to identify vulnerable third-party libraries, open-source dependencies, outdated components, and software supply chain risks.
- Infrastructure as Code Security: Understand how to assess infrastructure configurations, identify misconfigurations, and incorporate security checks into automated infrastructure deployment.
- Container and Kubernetes Security: Explore container image scanning, runtime protection, configuration security, access controls, and security considerations for container orchestration environments.
- Cloud Security Integration: Learn how security controls, identity management, configuration monitoring, and workload protection can be incorporated into cloud-based development and deployment processes.
- Secrets and Access Management: Understand how to protect credentials, API keys, tokens, certificates, and other sensitive secrets used in software development and deployment.
- Vulnerability Management and Remediation: Learn how to prioritize security findings, assess potential impacts, coordinate remediation, and verify that identified vulnerabilities have been addressed.
- Security Automation and Policy Enforcement: Explore how automated controls, policy checks, and security gates can help enforce security requirements consistently across development workflows.
- Software Supply Chain Security: Understand the importance of dependency management, artifact integrity, provenance, and protection against software supply chain attacks.
- Security Monitoring and Incident Response: Learn how logging, monitoring, alerting, and incident response practices support the detection and investigation of security issues in deployed applications.
- Compliance and Security Metrics: Understand how audit trails, security metrics, reporting, and compliance checks support secure software delivery and continual improvement.
- DevSecOps Culture and Collaboration: Explore how development, security, and operations teams can share responsibility for security and improve communication throughout the software lifecycle.